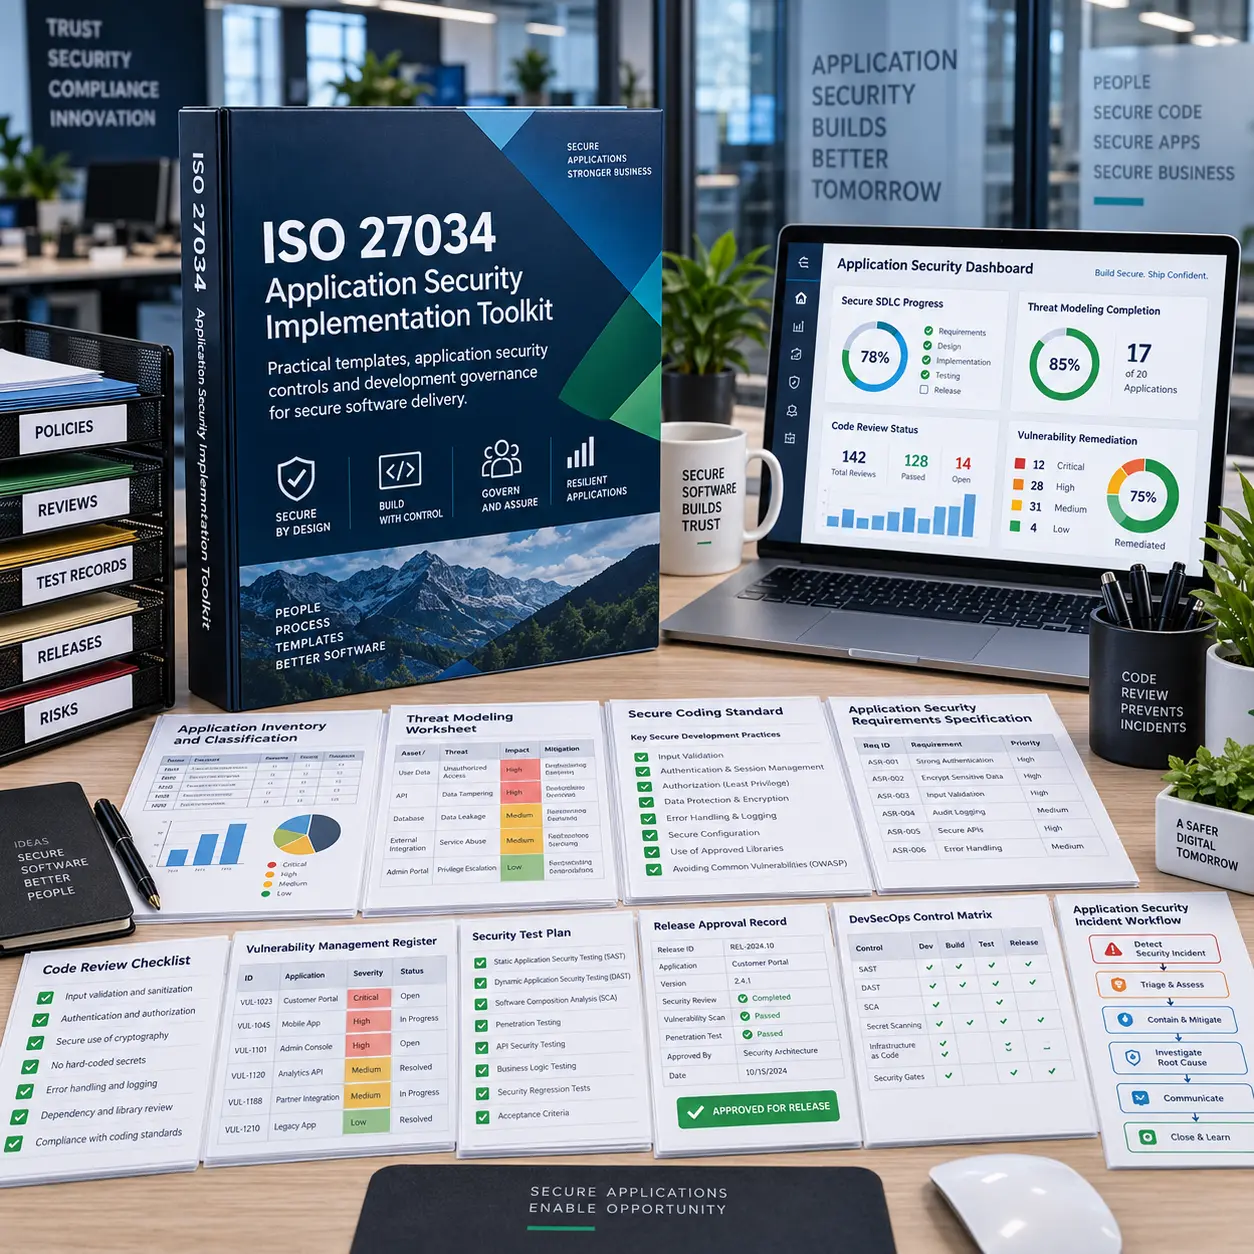
The ISO/IEC 27034 Application Security Implementation Toolkit provides a comprehensive, practical set of editable templates and professionally structured implementation resources to help organizations integrate application security into governance, risk management, software development, acquisition, operation, maintenance, and continual improvement activities.
Aligned with the ISO/IEC 27034 application security framework, this toolkit translates application security concepts into usable governance documents, secure SDLC procedures, risk assessments, control specifications, application normative framework tools, testing records, DevSecOps checklists, supplier controls, incident-readiness resources, audit evidence, and management reporting. It helps organizations build repeatable application security practices across internally developed, acquired, outsourced, cloud-hosted, and business-critical applications.
Building a consistent application security program can be demanding, particularly where organizations manage multiple development teams, legacy and cloud applications, third-party software, APIs, DevSecOps pipelines, regulatory obligations, security testing activities, and application-specific risks across the full lifecycle.
The ISO/IEC 27034 Application Security Implementation Toolkit provides a comprehensive collection of editable application security templates and structured implementation documents in Word, Excel, and PowerPoint formats. It helps your organization establish governance, define normative frameworks, integrate secure SDLC practices, manage application risks, design and verify controls, coordinate testing, strengthen incident readiness, organize audit evidence, and improve application security performance with greater consistency and control.
Below is the structured ISO 27034 document index extracted from the supplied package index. Use the quick navigation or expand each part to review the application security files before downloading the index file.
 Part 1. Engagement Initiation & Program Mobilization
 ISO IEC 27034 Implementation Project Charter.docx Application Security Implementation Roadmap.docx Consulting Engagement Scope Statement.docx Executive Sponsorship Brief.docx Project Governance Structure.docx Project Communication Plan.docx Project Kick-off Meeting Agenda.docx Project Meeting Minutes.docx Project Deliverables Acceptance Form.docx Change Request Form.docx Project Closure Report.docx
 Stakeholder Register.xlsx Implementation Roles and Responsibilities Matrix.xlsx RACI Matrix.xlsx Project Action Log.xlsx Project Risk and Issue Register.xlsx Project Assumption and Constraint Log.xlsx Project Status Report.xlsx
 Project Kick-off Presentation.pptx Steering Committee Report.pptx
Part 2. Organizational Context & Application Security Governance
Organizational Context Analysis.docx Business Unit Application Security Profile.docx Application Security Governance Framework.docx Application Security Policy.docx Application Security Management System Scope.docx Application Security Objectives.docx Application Security Principles.docx Application Security Governance Committee Charter.docx Enterprise Application Security Operating Model.docx Application Security Governance Meeting Agenda.docx Application Security Governance Meeting Minutes.docx Application Security Management Review Report.docx Application Security Governance Improvement Plan.docx Application Security Decision Rights Matrix.xlsx Application Security Accountability Matrix.xlsx Application Security Authority and Escalation Matrix.xlsx Application Security Governance KPI Dashboard.xlsx Application Security Governance Executive Briefing.pptx
Part 3. ISO IEC 27034 Gap Assessment & Baseline Review
ISO IEC 27034 Gap Assessment Plan.docx ISO IEC 27034 Gap Assessment Checklist.docx Current State Assessment Questionnaire.docx Application Security Maturity Assessment.docx Application Security Capability Assessment.docx Existing Controls Review.docx Secure SDLC Assessment.docx Application Security Documentation Review Checklist.docx Interview Guide for Business Owners.docx Interview Guide for IT and Development Teams.docx Interview Guide for Security Teams.docx Gap Assessment Report.docx Remediation Roadmap.docx ISO IEC 27034 Clause Mapping Assessment.xlsx Application Portfolio Security Baseline.xlsx Gap Assessment Evidence Register.xlsx Gap Assessment Findings Log.xlsx Gap Prioritization Matrix.xlsx Gap Assessment Executive Presentation.pptx
Part 4. Application Inventory & Classification
Application Registration Form.docx Application Business Criticality Assessment.docx Application Data Classification.docx Application Risk Classification.docx Application Architecture Profile.docx Application Technology Stack Profile.docx Enterprise Application Inventory.xlsx Application Ownership Register.xlsx Application Dependency Mapping.xlsx Third-party Application Register.xlsx Cloud Application Register.xlsx Legacy Application Register.xlsx Internet-facing Application Register.xlsx Crown Jewel Application Identification.xlsx Application Lifecycle Status Register.xlsx Application Decommissioning Candidate Register.xlsx Application Portfolio Classification Summary.pptx
Part 5. Organizational Normative Framework
Organizational Normative Framework Definition.docx Secure Architecture Standard.docx Secure Coding Standard.docx Secure Configuration Standard.docx Secure API Development Standard.docx Secure Mobile Application Standard.docx Secure Cloud Application Standard.docx Secure DevOps Standard.docx Cryptography Usage Standard.docx Authentication and Authorization Standard.docx Logging and Monitoring Standard.docx Data Protection Standard for Applications.docx Privacy by Design Requirement.docx Normative Framework Approval Form.docx Application Security Policy Set Register.xlsx Application Security Standards Register.xlsx Application Security Procedures Register.xlsx Application Security Guidelines Register.xlsx Application Security Control Library.xlsx Application Security Requirement Catalogue.xlsx Regulatory and Legal Requirement Mapping.xlsx Normative Framework Review Log.xlsx Organizational Normative Framework Overview.pptx
Part 6. Application Security Risk Management
Application Security Risk Management Procedure.docx Application Security Risk Assessment Methodology.docx Application Risk Assessment Plan.docx Application Risk Assessment Questionnaire.docx Threat Identification.docx Vulnerability Identification.docx Business Impact Assessment.docx Risk Treatment Plan.docx Risk Acceptance Form.docx Risk Exception Request.docx Residual Risk Review.docx Risk Escalation Form.docx Risk Review Meeting Minutes.docx Risk Scenario Register.xlsx Application Risk Register.xlsx Application Risk Rating Matrix.xlsx Risk Ownership Register.xlsx Application Security Risk Dashboard.xlsx Application Security Risk Executive Report.pptx
Part 7. Application Security Controls Design
Application Security Control Selection Procedure.docx Application Security Control Objective.docx Application Security Control Specification.docx Control Implementation Plan.docx Preventive Control Design.docx Detective Control Design.docx Corrective Control Design.docx Manual Control Design.docx Automated Control Design.docx Control Testing Procedure.docx Control Effectiveness Assessment.docx Control Improvement Plan.docx Application Security Control Catalogue.xlsx Control Applicability Matrix.xlsx Security Control Traceability Matrix.xlsx Control Owner Assignment Register.xlsx Control Exception Register.xlsx Application Security Controls Design Summary.pptx
Part 8. Application Normative Framework
Application Normative Framework.docx Application-specific Security Requirements.docx Application Security Target Profile.docx Application Security Acceptance Criteria.docx Application Security Baseline Configuration.docx Application Security Architecture Decision Record.docx Application-specific Risk Treatment Plan.docx Application Security Control Implementation Evidence.docx Application Security Control Verification Checklist.docx Application Normative Framework Approval Form.docx Application-specific Control Set.xlsx Application Security Requirement Traceability Matrix.xlsx Application Normative Framework Review Log.xlsx Application Normative Framework Summary.pptx
Part 9. Secure SDLC Integration
Secure SDLC Policy.docx Secure SDLC Procedure.docx Secure SDLC Phase Gate Checklist.docx Security Requirements Elicitation.docx Security Requirements Specification.docx Security User Story.docx Security Acceptance Criteria.docx Secure Design Review Checklist.docx Threat Modeling Procedure.docx Threat Modeling Worksheet.docx Attack Surface Analysis.docx Secure Coding Checklist.docx Code Review Checklist.docx Static Application Security Testing Procedure.docx Dynamic Application Security Testing Procedure.docx Software Composition Analysis Procedure.docx Infrastructure as Code Security Review.docx Container Security Review Checklist.docx CI/CD Security Control Checklist.docx Security Defect Management Procedure.docx Security Gate Approval Form.docx Release Security Readiness Checklist.docx Security Defect Register.xlsx Secure SDLC Integration Overview.pptx
Part 10. Architecture & Design Security
Application Security Architecture Review Procedure.docx Application Architecture Review Checklist.docx Security Architecture Diagram.docx Data Flow Diagram.docx Trust Boundary Diagram.docx Authentication Design Review.docx Authorization Design Review.docx Session Management Design Review.docx API Security Design Review.docx Cryptographic Design Review.docx Logging and Monitoring Design Review.docx Data Protection Design Review.docx Secure Integration Design Review.docx Cloud Security Architecture Review.docx Microservices Security Architecture Review.docx Zero Trust Application Architecture Review.docx Architecture Risk Decision Record.docx Architecture Exception Register.xlsx Application Security Architecture Review Presentation.pptx
Part 11. Supplier, Third-party & Outsourced Development Management
Supplier Application Security Requirement.docx Third-party Software Security Assessment.docx Supplier Security Due Diligence Questionnaire.docx Outsourced Development Security Agreement.docx Secure Development Contract Clause.docx Supplier Security Review Checklist.docx Supplier Vulnerability Disclosure Requirement.docx Supplier Corrective Action Plan.docx Supplier Security Responsibility Matrix.xlsx Third-party Component Inventory.xlsx Open-source Component Register.xlsx Software Bill of Materials.xlsx Third-party Risk Assessment.xlsx Supplier Security Evidence Register.xlsx Supplier Non-conformance Register.xlsx Supplier Application Security Management Summary.pptx
Part 12. Application Security Testing & Verification
Application Security Testing Strategy.docx Application Security Test Plan.docx Security Test Case.docx SAST Execution Report.docx DAST Execution Report.docx IAST Execution Report.docx SCA Execution Report.docx Penetration Testing Scope.docx Penetration Testing Rules of Engagement.docx Penetration Testing Report.docx API Security Testing Checklist.docx Mobile Application Security Testing Checklist.docx Cloud Application Security Testing Checklist.docx Secure Configuration Testing Checklist.docx Authentication Testing Checklist.docx Authorization Testing Checklist.docx Input Validation Testing Checklist.docx Business Logic Testing Checklist.docx Security Test Closure Report.docx Security Test Evidence Register.xlsx Security Test Defect Log.xlsx Application Security Testing Results Presentation.pptx
Part 13. Vulnerability & Defect Management
Application Vulnerability Management Procedure.docx Vulnerability Intake Form.docx Vulnerability Triage Checklist.docx Vulnerability Severity Rating Matrix.docx Vulnerability Remediation Plan.docx Vulnerability Exception Request.docx Vulnerability Risk Acceptance Form.docx Vulnerability Retesting Checklist.docx Vulnerability Closure Evidence.docx Critical Vulnerability Escalation Form.docx lnerability Escalation Form.docx Vulnerability Management Review Report.docx Vulnerability Register.xlsx Vulnerability Aging Report.xlsx SLA Compliance Dashboard.xlsx Vulnerability Management Executive Report.pptx
Part 14. DevSecOps & Automation
DevSecOps Operating Model.docx DevSecOps Control Framework.docx CI/CD Security Pipeline Design.docx Automated Security Testing Configuration.docx Secret Management Checklist.docx Infrastructure as Code Security Checklist.docx Container Image Security Checklist.docx Kubernetes Security Checklist.docx Build Integrity Checklist.docx Deployment Approval Workflow.docx Security Toolchain Inventory.xlsx Pipeline Security Gate Matrix.xlsx Security Automation Exception Register.xlsx DevSecOps Metrics Dashboard.xlsx DevSecOps Continuous Improvement Backlog.xlsx DevSecOps Automation Overview.pptx
Part 15. Identity, Access & Application Authorization
Application Access Control Policy.docx Role-based Access Control Design.docx Access Request Form.docx Access Approval Workflow.docx User Provisioning Procedure.docx User Deprovisioning Procedure.docx OAuth and Token Management Checklist.docx Application Authentication Configuration Checklist.docx Application Authorization Review Report.docx Application Access Control Matrix.xlsx Privileged Access Matrix.xlsx Segregation of Duties Matrix.xlsx Access Recertification Checklist.xlsx Service Account Register.xlsx API Key Register.xlsx Application Identity and Access Management Summary.pptx
Part 16. Data Protection, Privacy & Cryptography
Application Data Protection Requirement.docx Privacy Impact Assessment.docx Data Retention Requirement.docx Data Masking Requirement.docx Data Encryption Requirement.docx Key Management Requirement.docx Sensitive Data Exposure Checklist.docx Secure Data Disposal Checklist.docx Data Transfer Security Checklist.docx Application Privacy by Design Checklist.docx Personal Data Processing Register.xlsx Data Flow and Privacy Mapping.xlsx Cryptographic Control Register.xlsx Data Protection Compliance Mapping.xlsx Application Data Protection and Privacy Summary.pptx
Part 17. Logging, Monitoring & Incident Readiness
Application Logging Standard.docx Application Monitoring Requirement.docx Security Event Logging Checklist.docx Audit Trail Requirement.docx Application Security Monitoring Use Case.docx SIEM Integration Requirement.docx Application Incident Response Playbook.docx Application Incident Classification Matrix.docx Security Incident Escalation Matrix.docx Incident Evidence Collection Checklist.docx Post-incident Review Report.docx Log Retention Matrix.xlsx Alert Prioritization Matrix.xlsx Lessons Learned Register.xlsx Application Incident Readiness Presentation.pptx
Part 18. Business Continuity, Resilience & Recovery
Application Resilience Requirement.docx Application Business Continuity Requirement.docx Application Disaster Recovery Requirement.docx Backup Requirement Checklist.docx Application Failover Test Plan.docx Application Recovery Test Report.docx Resilience Risk Assessment.docx High Availability Design Checklist.docx Application Continuity Exercise Report.docx Recovery Time Objective Matrix.xlsx Recovery Point Objective Matrix.xlsx Application Resilience and Recovery Summary.pptx
Part 19. Awareness, Training & Competency
Application Security Training Plan.docx Developer Competency Assessment.docx Security Champion Program Charter.docx Security Champion Role Description.docx Security Champion Activity Plan.docx Application Security Awareness Material.docx Training Effectiveness Evaluation.docx Competency Gap Assessment.docx Competency Improvement Plan.docx Secure Coding Training Matrix.xlsx Role-based Application Security Training Matrix.xlsx Training Attendance Register.xlsx Application Security Awareness Training Deck.pptx Security Champion Program Presentation.pptx
Part 20. Compliance, Audit & Evidence Management
Application Security Audit Plan.docx Internal Audit Checklist.docx Control Evidence Collection Checklist.docx Audit Sampling Plan.docx Audit Interview Guide.docx Nonconformity Report.docx Corrective Action Request.docx Corrective Action Plan.docx Corrective Action Verification.docx Management Review Evidence Pack.docx External Audit Readiness Checklist.docx ISO IEC 27034 Compliance Register.xlsx Audit Evidence Register.xlsx Audit Finding Log.xlsx Compliance Dashboard.xlsx Audit Readiness Executive Presentation.pptxUse these quick links to review the full file list and payment instructions.
| Date File Updated | 25/03/2025 |
| File Format | pdf, xls, doc, docx, xlsx, pptx |
| No. of files | 364 File; 20 Folders |
| File download size | 98.06 MB (.rar) |
| Language |
 English |
| Purchase code | ISO27034-Toolkits |
The ISO 27034 toolkit helped our development and security teams agree on one application security process. The governance, risk and secure SDLC templates gave us a clear structure without forcing us to redesign our existing engineering workflow.
We used the toolkit to formalize application inventories, ownership, security requirements and evidence tracking. It made application security responsibilities much easier to communicate to product managers and engineering teams.
The risk assessment and application control templates are practical and easy to tailor. They helped us connect business impact, threats, vulnerabilities, treatment actions and control verification in one consistent process.
The secure SDLC and architecture review documents were the most useful parts for us. They provided a solid baseline for threat modeling, design reviews, security requirements and release-readiness checks.
Our DevSecOps team adapted the CI/CD security gates, automated testing and vulnerability management templates very quickly. The toolkit gave us a better way to document controls that were already running in our pipelines.
A very comprehensive application security toolkit. The document structure helped us organize supplier security, open-source component records, software bills of materials and third-party risk evidence more consistently.
The toolkit made our application security audit preparation much more structured. Evidence registers, control mappings, findings logs and corrective action templates were especially helpful for internal review meetings.
I found the application normative framework materials very useful. They helped us define application-specific security requirements and acceptance criteria instead of relying only on high-level information security policies.
The vulnerability management section gave our teams a common language for severity, remediation, exceptions, retesting and closure. It reduced confusion between security and engineering during issue management.
The incident-readiness and logging templates were easy to integrate with our SOC procedures. They helped application owners understand what evidence, escalation paths and monitoring requirements were expected from them.
We used the continuity and resilience templates for several critical applications. The RTO/RPO matrices, recovery testing and application resilience records helped us align security with business continuity planning.
The training, security champion and competency templates were useful for rolling application security responsibilities out beyond the central security team. They provided a practical structure for developers, architects and application owners.