ISO Audit Preparation
An evidence led guide to planning ISO internal audits, preparing for independent certification assessments, and demonstrating that management system controls work in everyday operations.
Organize audit scope, processes, people, records and corrective actions before the audit. Use the step by step guidance below to test readiness, identify gaps and verify that improvements are effective, not merely documented.
Risk based audit planning and traceable objective evidence
Practical readiness checks for process owners and auditors
Follow through from findings to verified corrective actions
Audit Readiness Focus Areas
Six connected workstreams establish whether the management system is understood, implemented and supported by reliable evidence.
Scope & Audit Criteria
Define the system boundaries, sites, shifts, outsourced activities and processes to be evaluated. Verify the applicable licensed standard edition, regulatory duties and audit objectives.
Controlled Information & Evidence
Locate approved procedures and real operating records, including risk reviews, results, nonconformities, actions and previous audit conclusions. Check traceability and retrieval.
People, Roles & Competence
Confirm that audit teams are competent and sufficiently impartial; prepare process owners to explain what they do, what decisions they make and how they respond to deviations.
Operational Controls & Sampling
Trace representative products, orders, cases or service transactions from start to finish. Sample across relevant periods, shifts, sites and significant risks.
Corrective Actions & Effectiveness
Distinguish an immediate correction from root cause based corrective action. Require evidence that completed actions prevent recurrence or reduce the identified cause.
Leadership & Management Review
Verify that management reviews audit results, performance, obligations, resource adequacy and opportunities for improvement, with accountable decisions and follow up.
ISO Audit Preparation Roadmap
This six stage working sequence connects preparation to audit execution and objective closure. Adapt it to the scope and type of assessment; it is not a prescribed certification timeline.
Define Scope & Criteria
Confirm what will be audited, why, against which references and at which locations; clarify audit authority, objectives and interfaces.
Review Risks & Evidence
Check process maps, documented information, obligations, previous findings and high risk activities before selecting samples.
Plan & Assign the Audit
Set an achievable timetable, auditors, interviewees, methods, sampling strategy, access permissions and reporting arrangements.
Interview & Verify Practice
Use interviews, observation and record trails to test process conformity rather than relying exclusively on written procedures.
Evaluate & Report Findings
Compare evidence with defined criteria; record clear, fair findings and communicate significant issues without delay.
Correct, Verify & Improve
Assign owners, evaluate causes, implement actions, verify effectiveness and bring unresolved risk to management review.
Detailed Audit Preparation Guidance
A practical walkthrough for auditors, management representatives and process owners. Each stage includes the actions to perform, typical evidence, accountable roles and a completion criterion.
01. Confirm the Audit Scope, Criteria and Objectives
Start by defining the audit purpose and the management system boundaries. Distinguish internal conformance assurance from a third party certification decision; confirm whether the work covers one process, a site, the whole system or selected changes.
Key audit preparation activities
Confirm the current applicable standard edition and any sector specific, contractual or legal criteria.
Map business activities, locations, shifts, functions, outsourced processes and critical interfaces into the audit scope.
Agree objectives, risk priorities, reporting recipients, responsibilities and needed auditor competence; protect independence and confidentiality.
02. Review Documentation, Processes and Existing Records
Perform a focused desk review before opening meetings or on site sampling. The presence of a template is not proof of conformity; inspect evidence that the described controls were actually operated over time.
Key audit preparation activities
Review policies, objectives, process maps, procedures and control of revisions and access at point of use.
Examine relevant risk and opportunity assessments, legal obligations, monitoring records, customer feedback and supplier controls.
Review previous internal/external findings, incident logs, action status, competency results and management review decisions.
03. Build a Risk Based Audit Plan and Checklist
Convert the scope into a feasible audit schedule. A good checklist supports inquiry while permitting the auditor to follow objective evidence and emerging risks.
Key audit preparation activities
Allocate time by process significance, prior performance, change, incident history and audit complexity.
Assign competent auditors independently of the work being audited where practicable, with interviewees, sites, methods and access arrangements.
Prepare process oriented questions and sampling routes; plan the opening meeting, observations, closing meeting and escalation of urgent issues.
04. Conduct Interviews, Observe Work and Sample Evidence
Auditors should triangulate explanations from personnel, direct observation and verifiable records. Sampling provides assurance within limits; it is not proof that every individual transaction conforms.
Key audit preparation activities
Ask process owners to describe actual inputs, outputs, criteria, risks, decisions, escalation and control responsibilities.
Observe real activities where safe and feasible; sample completed records across relevant dates, shifts, sites and exception cases.
Follow an end to end trail such as Order → Procurement → Receipt → Operation → Verification → Release → Customer Feedback.
05. Record Findings and Communicate Audit Conclusions
Classify the results against the agreed criteria and available objective evidence. A nonconformity needs a clear unmet requirement, an evidence trail and a factual statement of the gap.
Key audit preparation activities
Separate conformities, nonconformities and observations using the audit programme’s defined categories; do not invent universal severity rules.
Record the source criterion, observed condition, record identifiers, sampling scope, process/site and possible impact.
Review factual accuracy with auditees, escalate critical safety or compliance concerns as required, and summarize balanced conclusions at closing.
06. Close Actions and Verify Corrective Action Effectiveness
The work is not complete when a new form has been issued. Distinguish containment or correction from analysis of the cause, systemic corrective action and verification of sustained effectiveness.
Key audit preparation activities
Prioritize findings, assign accountable owners and dates, evaluate extent and causes, and control any immediate exposure.
Implement proportionate changes in procedures, equipment, systems, competence or controls; gather new operating evidence.
Verify actions using post change samples or performance trends, then report remaining risks and overdue items to management review.
Key Evidence to Prepare Before an ISO Audit
Gather records by management system purpose rather than by folder count. Each item below is illustrative and must be adapted to the chosen standard and documented scope.
Governance & Scope
Approved scope and policy, context/interested party reviews, process map, organizational roles, objectives and leadership communication.
Risk & Compliance
Risk methods and registers, relevant legal/other obligations, impact or hazard assessments, risk treatments, changes and follow up monitoring.
Operational Execution
Completed production, service, delivery, inspection, maintenance, validation, incident, traceability and release records as relevant to the activity.
People & Suppliers
Competence criteria, training effectiveness, worker consultation where relevant, supplier evaluation, contractor controls and outsourced process records.
Performance & Improvement
KPI results, trend reviews, customer/stakeholder feedback, incidents and complaints, corrective actions and effectiveness checks.
Assurance & Leadership
Risk based internal audit programme, completed audits, finding closure, management review inputs, decisions, action owners and follow up.
Verify the System Where Work Happens
Reliable auditing follows the process from an initiating request through execution, control, review and final output. Pair interviews with representative operational samples; avoid treating an approved document as a substitute for an implemented control.
Sample higher risk work, exceptions and recent changes, not only routine successful cases.
Cross check what personnel describe against actual work and record timestamps.
Protect confidentiality, safety and production continuity during on site or remote work.
Worked trail: Select a completed production order; confirm approved instructions, operator competence, incoming material checks, in process control, release decision and any nonconformity resolution. Replace this example with a corresponding service or digital workflow where appropriate.
Internal Audits vs. Certification Audits
Audit approaches have different objectives. Do not interpret this page as a fixed certification schedule or as authorization to award or guarantee ISO certification.
Internal Audit
Organization led assurance, based on its defined programme and relevant audit criteria. Focus on conformity, process performance, risk and opportunities to improve; preserve auditor objectivity.
Initial Certification: Stage 1
The certification body evaluates preparedness, scope and relevant system information and plans Stage 2. The detailed approach and outcomes depend on its accredited certification rules.
Initial Certification: Stage 2
The certification body evaluates implementation and effectiveness using interviews, operations and evidence. Certification decisions are made by the independent certification body, not ISO Toolkits.
Surveillance & Recertification
Maintain controls, records and improvement between visits. Confirm the certification body’s programme, significant changes, previous findings and any edition transition arrangements.
Practical ISO Audit Readiness Checklist
A compact pre audit screening tool for team leaders, quality/compliance coordinators and internal auditors.
Use each checkpoint as Ready / Partly Ready / Not Ready / Not Applicable with a reason, evidence reference, accountable owner and target date. The list supports screening; it does not replace audit criteria from the applicable standard.
Scope is defensible: Sites, products/services, processes, exclusions and outsourced functions are mapped; scope is approved and corresponds to current work.
Applicable criteria are current: The correct published edition, relevant statutory duties and certification body/sector rules have been confirmed.
Processes have accountable owners: Individuals can explain controls, decision points, escalations and records for processes they actually operate.
Records are usable: Samples are legible, attributable, accessible, current and protected, with correct dates and identifiers.
Risks are translated into controls: Risk and obligation evaluations are connected to operating instructions, responsibilities, monitoring and responses.
Performance is reviewed: Objectives, metrics, process results, incidents and customer/stakeholder feedback lead to meaningful decisions.
Audit programme has been completed appropriately: Internal audits cover the approved programme using competent and appropriately impartial auditors, with documented findings.
Corrective actions are verified: Prior findings have root cause evaluation and evidence of appropriate action and effectiveness checks.
Leadership review leads to action: Management review considers relevant inputs, resource decisions, changes, action owners and follow up status.
Information security and confidentiality are protected: Audit information access, remote review, personal data and confidential records are handled under appropriate controls.
From Nonconformity to Verified Closure
Audit findings add value only when they lead to proportionate correction, cause analysis, preventive system changes and verified results.
1. Contain & Correct
Protect customers, employees, information or processes from an immediate identified problem. Keep correction distinct from a lasting systemic fix.
2. Investigate Extent & Cause
Determine where similar problems may exist, which controls failed, why they failed and whether an underlying system weakness contributed.
3. Implement the Corrective Action
Assign a responsible owner, due date, necessary resources and change controls; update the procedure or system where the evidence supports it.
4. Verify Sustained Effectiveness
Repeat relevant sample tests or analyze post change performance to check that the action works in daily operation and has not created new risks.
Example: An auditor finds obsolete work instructions in use. Immediate correction replaces withdrawn copies. Root cause analysis identifies an unreliable document distribution workflow. The corrective action updates point of use access and withdrawal controls; effectiveness is checked by sampling shifts and locations after deployment.
Standard Specific Audit Evidence Priorities
Shared management system arrangements can be audited coherently, but requirements differ across standards. Verify requirements using the applicable licensed edition and relevant regulations.
ISO 9001 · Quality
Trace customer requirements, order changes, supplier and purchasing controls, product/service release, complaints, nonconforming outputs and effectiveness of improvement.
ISO 14001 · Environment
Connect environmental aspects, compliance obligations, operating controls, monitoring, emergency preparedness and environmental performance to evidence.
ISO 45001 · OH&S
Examine hazard controls, worker consultation and participation, contractor risks, competence, incident investigation and operational implementation.
ISO/IEC 27001 · Information Security
Review the defined ISMS scope, information security risks, risk treatment, Statement of Applicability, selected controls and effectiveness evidence.
ISO 22000 · Food Safety
Review hazard analysis, operational prerequisite/PRP controls as applicable, traceability, monitoring, corrections and food safety verification.
ISO 13485 · Medical Devices
Assess applicable regulatory requirements, risk related controls, traceability where required, validation, suppliers, complaints and CAPA records.
Illustrative 30-Day Audit Readiness Plan
This is an adaptable improvement sprint, not a mandatory ISO or certification body timetable. Complex systemic gaps, insufficient operating history or regulatory issues can require substantially longer.
Days 01 to 07 · Establish Baseline
Confirm scope, current edition, prior findings, key risks and accountable teams. Choose a representative set of records and make a prioritized gap register.
Days 08 to 14 · Address Major Gaps
Implement risk ranked fixes, document controls, overdue actions and competence interventions. Communicate updated responsibilities.
Days 15 to 21 · Test Implementation
Conduct internal audit samples, observe actual work, record findings and verify whether newly implemented controls are functioning.
Days 22 to 30 · Verify & Escalate
Recheck corrective action effectiveness, review unresolved exposure with leadership and set realistic follow up commitments.
Audit Preparation Tools & Further Guidance
Connect audit planning and evidence review with implementation templates, relevant management system guidance and authoritative standards references.
Audit Checklists & Document Control
Use structured checklists and review existing approval, revision, access and retention controls.
ISO Implementation Guides
Translate identified weaknesses into owners, tasks, documentation and operating evidence.
Common Implementation Mistakes
Understand recurrent causes of weak records, incomplete controls and ineffective corrective actions.
Further Reading & Professional References
ISO 19011:2026, Guidelines for auditing management systems ↗
IAF MD 5, Determination of audit time for management systems ↗
ISO 19011 provides audit guidance; it is not itself a certification scheme. Requirements of a chosen ISO management system standard and accredited certification body rules must be verified separately. ISO Toolkits is an independent implementation resource provider and is not affiliated with ISO.
Prepare for ISO Audits with Structured, Editable Resources
Browse practical toolkits that support audit programmes, checklists, records, management review, nonconformity analysis and corrective action tracking. Tailor each template to your processes, chosen standard and audit objectives.
Connect criteria to real process evidence and responsible owners.
Keep evidence, findings and effectiveness checks in a traceable system.
Speed Up ISO Implementation
with Ready Made Documentation
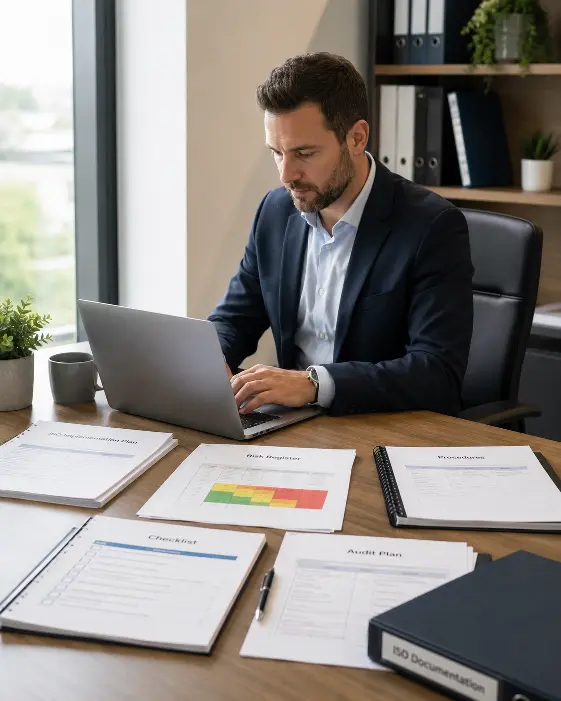
Access editable ISO templates, procedures, forms, registers, and audit checklists to reduce manual work and prepare faster with confidence.
The templates gave us a well-organized management system that is professional, accessible, and easy for process owners to use.
Our teams and auditors responded positively. The toolkit helped us present our processes in a structured and professional way.
The toolkit provides a flexible best-practice framework that keeps our documentation aligned as requirements evolve.
We saved significant time preparing our policies, procedures, forms, and internal audit materials for the implementation project.
The documentation was clear, professional, and easy to adapt. It gave our team a much stronger starting point.
A practical toolkit for consultants who need a repeatable and organized approach to ISO implementation documentation.
The toolkit helped us organize our health and safety documents into a more practical and ready for implementation structure.
The templates were easy to customize and gave us a clear foundation for building a client-ready ISO management system.
The audit checklists were practical and helped our team review gaps before the external audit preparation stage.
We appreciated the clear structure. It made implementation planning easier and helped our department owners understand their role.
The documentation package saved our team time and reduced the need to create ISO forms and registers from the beginning.
The toolkit gave us a professional starting point and helped us improve consistency across procedures, records, and checklists.
Trusted by over 10,000+ Client Organizations
We have provided ISO Implementation Toolkits to over 10,000 businesses and organizations of all sizes, from startups and small businesses to the Fortune 100, in over 130 countries.